Why Blame and “Human Error” Are Putting Your Business at Risk
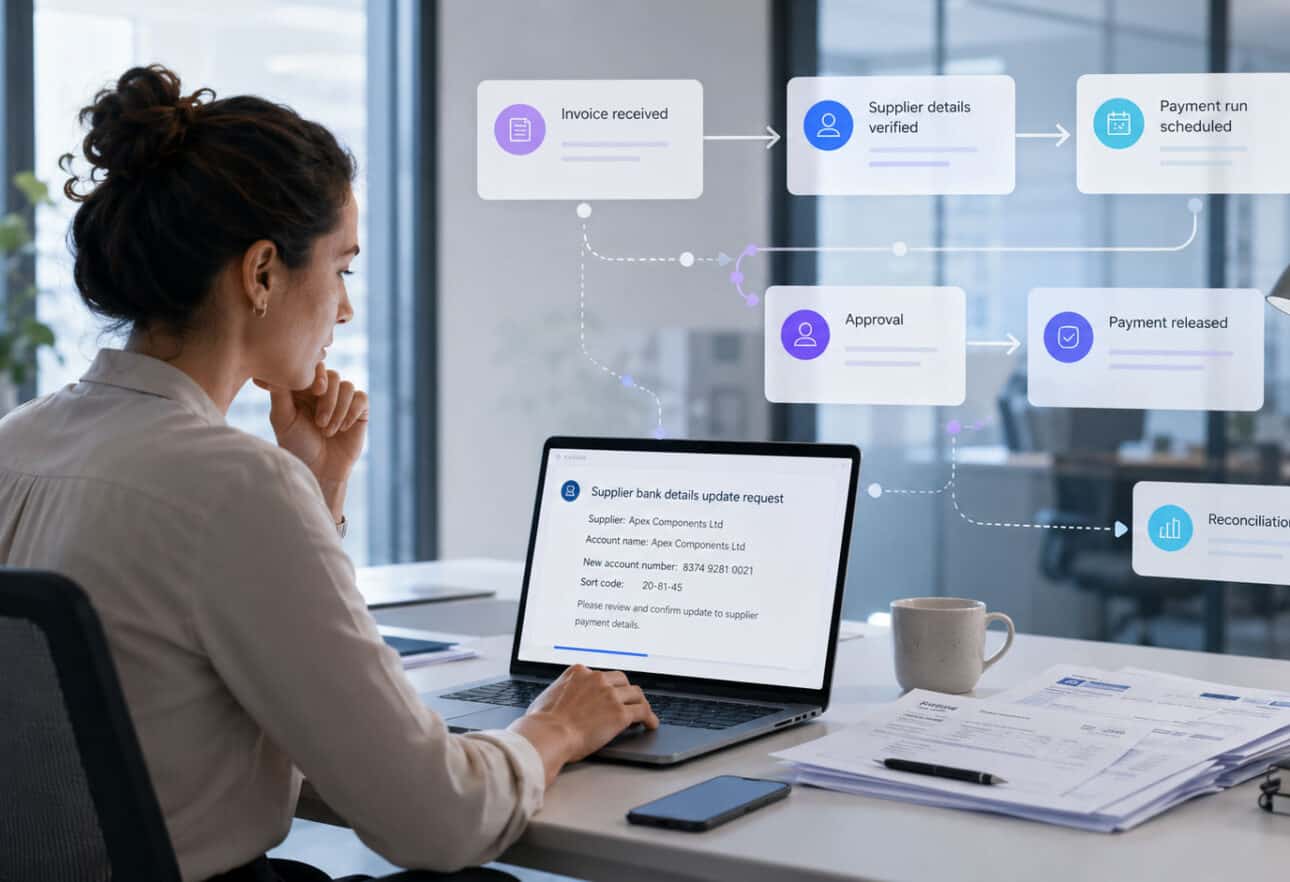
A finance team is trying to finish the month-end payment run. Dave has a list of invoices open, a supplier has already chased twice, and the team wants to avoid […]
A finance team is trying to finish the month-end payment run. Dave has a list of invoices open, a supplier has already chased twice, and the team wants to avoid […]
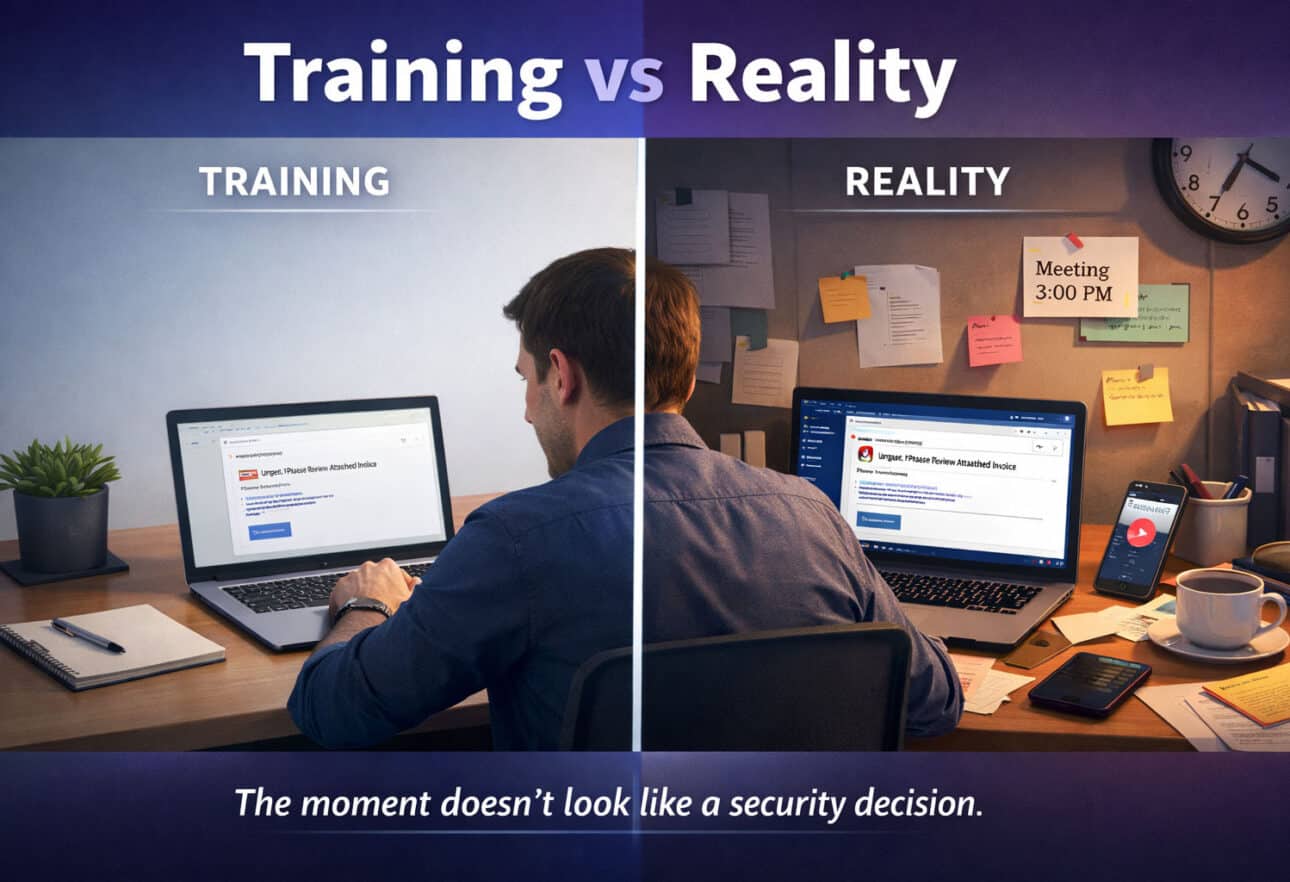
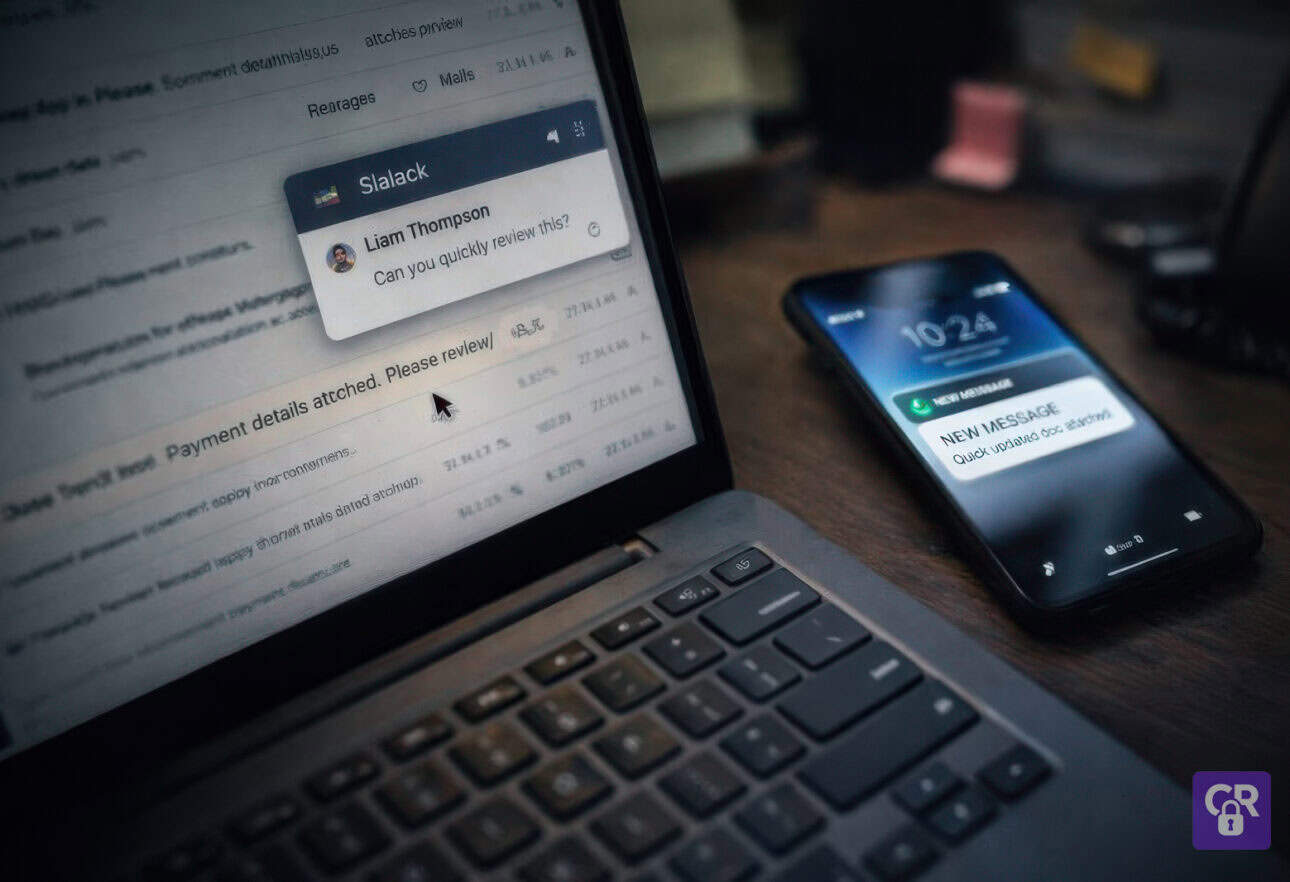
The Moment That Doesn’t Look Like Risk A message comes through on Teams. It appears to be from someone senior: short, direct, and straightforward. They need something sorted quickly. There […]
The Reality of Workplace Decisions There’s an assumption built into most cybersecurity training. That when an employee is faced with something suspicious, they will recognise the moment, pause what they […]
In our previous article, Why Knowledge Alone Isn’t Enough, we explored why traditional cybersecurity awareness training often fails to prevent real-world cyber incidents. Cybersecurity incidents are frequently attributed to human […]
Cybersecurity has become part of everyday conversation in modern organisations. Major ransomware attacks, data breaches, and online fraud incidents are now widely reported in the news, and most employees are […]
Charities occupy a unique position within society. They exist to support communities, protect vulnerable individuals, and address challenges that many other organisations are not equipped to handle. From local community […]
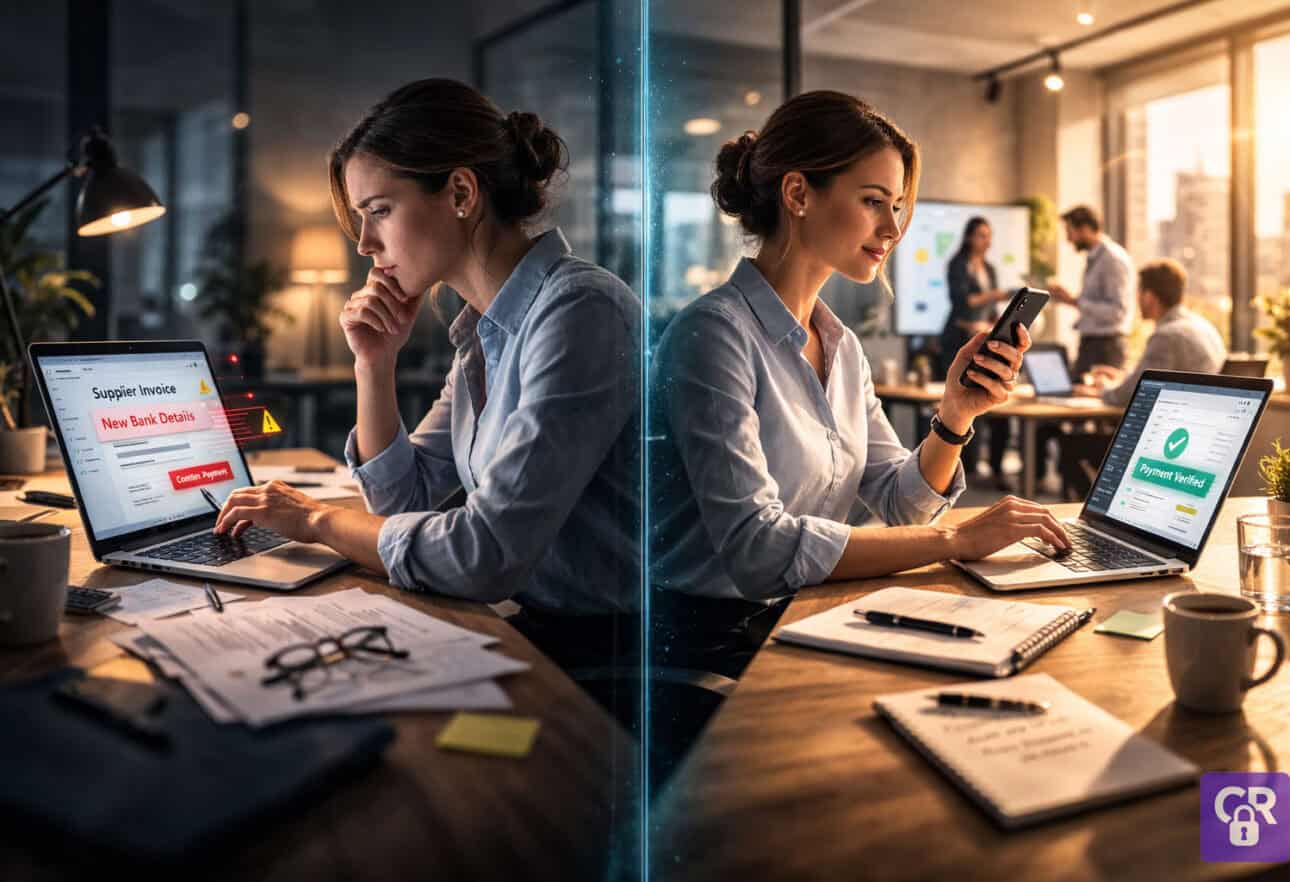
A finance assistant receives an email from a long-standing supplier. The tone is familiar. The branding is correct. The request is straightforward: bank details have changed, and future payments should […]
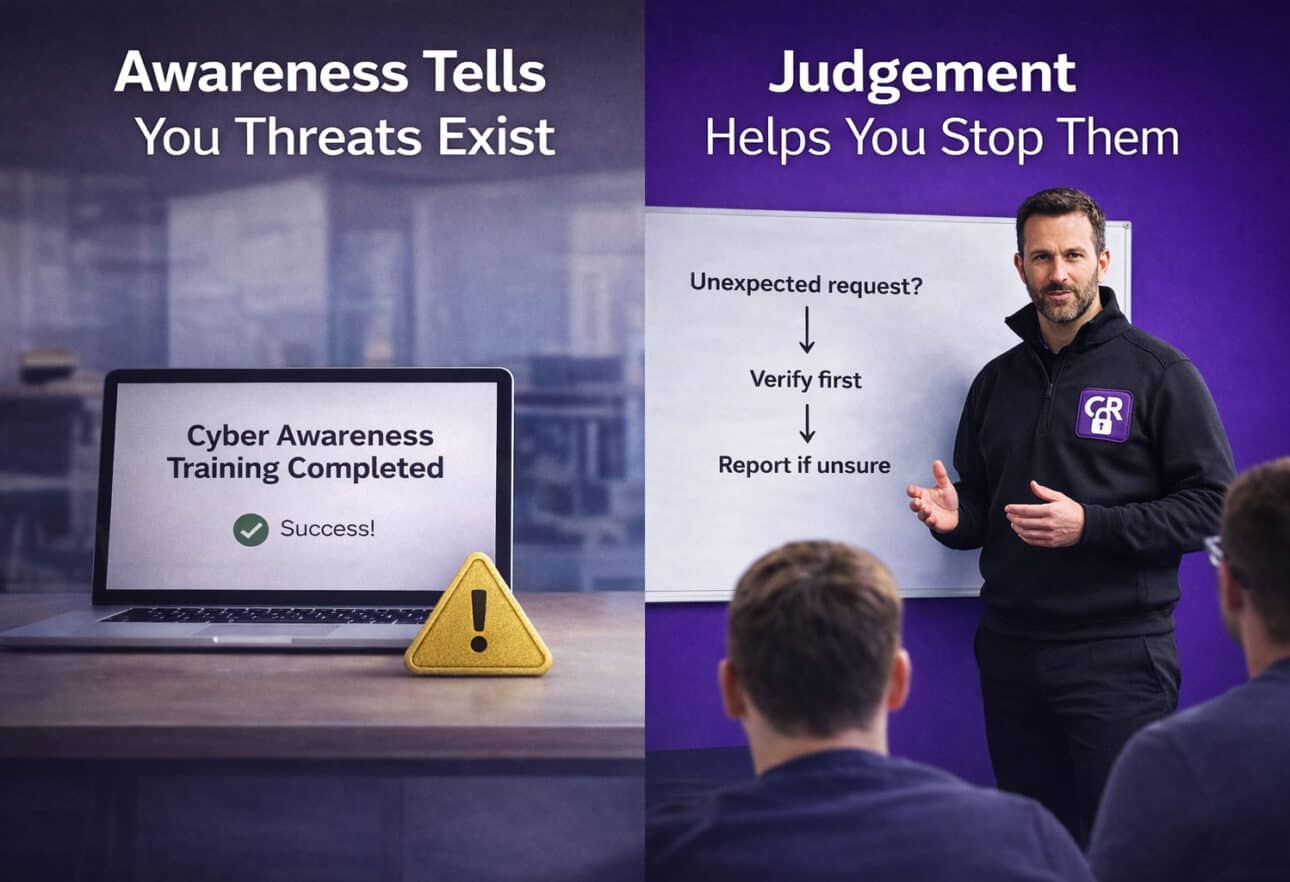
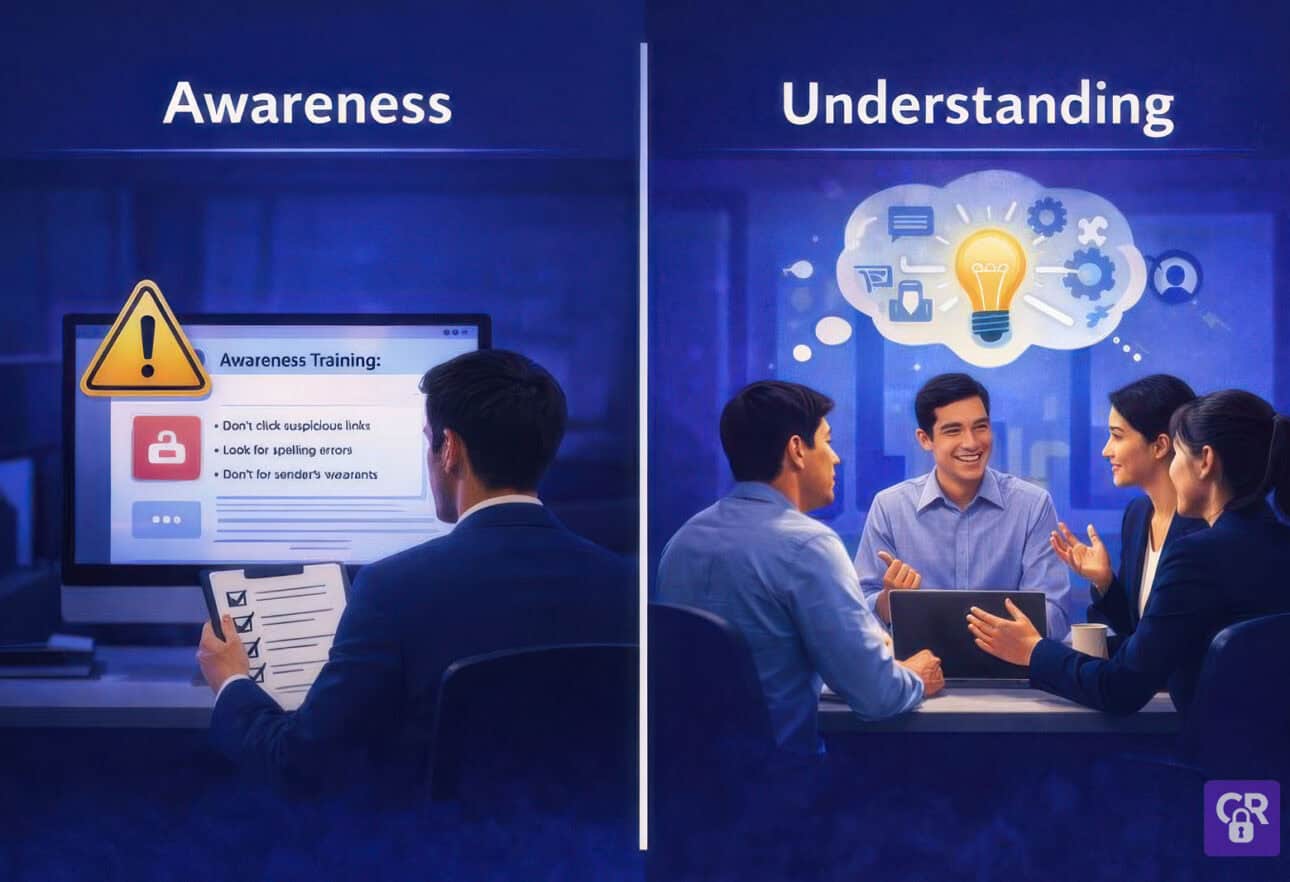
For a long time, cybersecurity awareness was treated as a reasonable endpoint. If staff had completed the training, clicked through the module, and acknowledged the policy, organisations could confidently say […]
Most cyber training is built on a quiet assumption: that when a security decision matters, people will have the time, focus, and mental space to make a good one. That […]
If you sit in enough meetings about risk, compliance, or “cyber”, you start to notice something interesting. The language changes, but the assumptions rarely do. Cybersecurity and information security are […]